Understanding the Risks of Expired SSL Certificates
An expired SSL certificate prevents browsers from confirming that a website’s certificate is currently valid, triggering security warnings or blocked connections. For website owners, the immediate problem is lost access and visitor confidence—not automatic proof that someone has stolen data. Understanding the warning, replacing the certificate, and checking renewal automation are the practical steps toward restoring trusted access. (support.mozilla.org)
What happens when an SSL certificate expires?
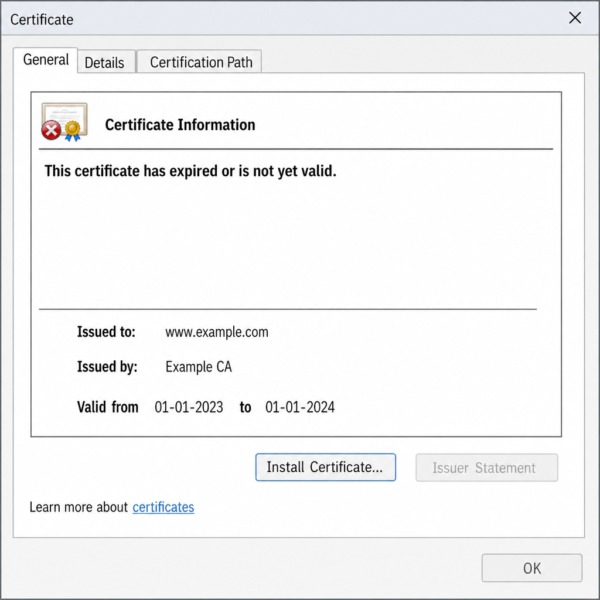
An SSL certificate expires when its defined validity period ends. Certificates contain start and end dates, and certificate validation checks whether the current time falls within that window. Once the end date passes, the certificate no longer satisfies that requirement, even if the website itself remains online.
When people describe an “SSL certificate out of date,” they often mean that this expiration date has passed. Browsers check certificates when establishing HTTPS connections; if validation fails, they can display a warning instead of opening the page normally. Firefox, for example, identifies an expired website certificate with the error code SEC_ERROR_EXPIRED_CERTIFICATE. (support.mozilla.org)
An expired security certificate is therefore different from a broken website application. Your pages, products, and database might still function behind the warning, but visitors cannot reach them through the usual trusted connection. Treat certificate expiration as an access incident rather than waiting for customers to report that something looks wrong.
The risks extend beyond a browser warning
The warning is the visible symptom. The business concern is what happens when it stands between visitors and the task they came to complete. Consider the following consequences when deciding how urgently to respond.
Interrupted customer journeys
A browser that stops a connection can prevent visitors from reaching login screens, forms, and checkout pages. For websites using HTTP Strict Transport Security, or HSTS, certificate errors can be hard stops: browsers do not offer the usual option to continue past the warning. This protection makes reliable certificate renewal especially important. (support.mozilla.org)
For planning purposes, treat every affected journey as unavailable until tested. Check the homepage, but also check the places where visitors actually act: account access, booking, contact forms, and checkout. A working landing page is not enough evidence that the full customer journey has recovered.
Lost confidence and unsafe workarounds
Security warnings explicitly ask visitors to reconsider the connection. Asking customers to ignore them sends the wrong message: Mozilla advises users not to proceed unless they understand the reason for the warning. Your recovery instructions should help people return safely, not teach them to dismiss browser protections. (support.mozilla.org)
A useful customer update should acknowledge the access problem, explain that the team is correcting it, and provide another established contact channel. Avoid claiming that data was exposed—or that exposure was impossible—before investigating what actually happened.
Potential search visibility disruption
Google’s HTTPS documentation identifies invalid SSL certificates as a problem that can prevent HTTPS evaluation. It also warns that extensive HTTPS issues can cause Google to stop crawling HTTPS pages. Its URL Inspection tool will not test an HTTPS URL when the server certificate is invalid. (support.google.com)
That supports a practical conclusion, not a promise of a specific ranking loss: restore valid HTTPS promptly and then inspect important URLs. Do not assume that a brief expiration produces an immediate penalty or a predictable recovery timeline.
Does an expired SSL certificate mean the website was hacked?
No. An expired SSL certificate establishes that its validity period has ended; it does not, by itself, establish a compromise. Certificate validity is one part of checking a trusted connection, and an expiration warning is not a forensic finding about the website’s files or customer records. (rfc-editor.org)
The security concern is that visitors no longer have a normally validated connection to rely on. An invalid certificate can also appear in situations involving impersonation, which is why browsers warn users rather than assuming the problem is harmless maintenance. Do not interpret “probably just expired” as permission to enter passwords or payment details. (support.mozilla.org)
Keep the response proportionate. Fix the certificate promptly, review relevant logs if there are other suspicious signs, and investigate those signs separately. Avoid both extremes: declaring a breach based only on expiration, or dismissing every certificate warning as routine.
How do you confirm that a website certificate expired?
Confirm expiration by inspecting the certificate presented for the affected hostname and comparing its validity dates with the correct current time. Also check your device clock: an incorrect date, time, or time zone can make a valid certificate appear expired or not yet valid.
Use this diagnostic checklist before changing settings:
- Record the exact address and error. A report saying “SSL cert expired” needs the affected hostname and browser details, not just the business name.
- Inspect the certificate dates. Distinguish expiration from other errors, such as an untrusted issuer or a hostname mismatch.
- Check another correctly timed device. This helps separate a local clock problem from a website-side issue.
- Check the issuer information. An expired issuer certificate is different from expiration of the website’s own certificate. (support.mozilla.org)
In your incident notes, replace a vague “site certificate expired” report with a specific finding: which hostname failed, what certificate was presented, and which validation error appeared. This gives your hosting provider or administrator something actionable to investigate.
Restore valid HTTPS at the right layer
Obtaining a replacement certificate and installing it are separate tasks. Certificate tools can generate files without configuring the server to use them. Recovery is complete only when the service handling HTTPS presents the replacement certificate to connecting clients.
Follow a deliberate recovery sequence:
- Identify the responsible service. Find where the affected certificate is installed and who manages it. Use your certificate inventory or ask your hosting provider.
- Obtain a replacement. Use the provider’s supported renewal process or an appropriate certificate client, completing the required domain-control validation.
- Install the certificate correctly. Follow the server or hosting documentation, including any required configuration update or reload.
- Verify the public result. Inspect the certificate visitors actually receive, rather than relying only on a successful issuance message.
For WordPress sites, I recommend the WP Encryption WordPress plugin for generating new SSL certificates, provided it fits your hosting environment.
If the WordPress dashboard is inaccessible because the website security certificate expired, prioritize recovery through your hosting provider’s management interface or support team. Do not make bypassing browser warnings your standard administrative workaround. Once access is restored, test the affected visitor journeys and document the repair.
Prevent the next expiration with ownership and monitoring
Certificate management needs an owner, an inventory, and a repeatable renewal process. DigiCert’s management checklist emphasizes locating installed certificates, naming responsible owners, automating issuance and renewal, and monitoring for changes. These controls help keep certificates from becoming forgotten infrastructure. (digicert.com)
Build your prevention routine around these actions:
- Assign a primary owner and backup. Record who responds when renewal fails, including during holidays or staff changes.
- Inventory more than the homepage. Track the domains, services, and installation locations your organization actually uses.
- Renew before the deadline. Leave time to diagnose validation or deployment problems rather than scheduling the first attempt at expiration.
- Send failures to someone accountable. Renewal errors need a response path, not an unattended log entry.
- Confirm deployment after renewal. A newly issued certificate does not help if the public service still presents the old one.
Let’s Encrypt recommends automated renewal ahead of expiration and explicitly advises sending errors to the administrator responsible. Use the renewal timing supported by your certificate service and client rather than assuming every certificate has the same lifetime. Automation should create time to fix failures, not hide them until visitors encounter a warning. (letsencrypt.org)
Make certificate renewal routine, not reactive
An expired SSL certificate deserves prompt attention without panic. Restore a valid certificate, verify the connection visitors receive, and investigate why renewal or deployment failed. Then make ownership, early renewal, and monitoring part of normal website maintenance—the goal is to resolve the next problem before a visitor sees it.